Advisory & Consulting
Cyber security consultancy and advisory
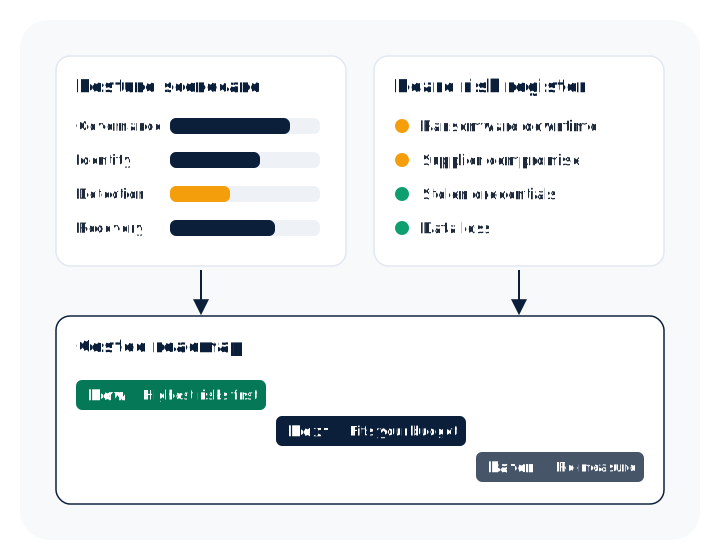
Independent advice, with no product to push: a clear-eyed assessment of where you stand, a risk picture your board can act on and a costed roadmap that fixes what matters first. Delivered by vetted specialist partners, with Threat Protect accountable throughout.
Definition
What does a cyber security consultancy do?
A cyber security consultancy gives an organisation senior, independent advice on its security risk. It works out where you stand, what matters most to the business and what to fix first, then turns that into a plan your board can fund. It does not replace your IT team. It gives them, and your leadership, a clear direction.
Threat Protect is vendor-agnostic, so the advice is not there to sell you a particular product. The work is delivered by vetted specialist partners. We scope it, select and contract the right people, oversee delivery and stay your single point of accountability.
When companies bring us in
If one of these sounds familiar, you’re in the right place.
“A client or our insurer wants ISO 27001 or a completed security questionnaire, and we can’t answer it honestly.”
“The board has asked how exposed we really are, and we need a straight answer, not a dashboard.”
“Security has outgrown being someone’s side job, but a full-time CISO isn’t justified yet.”
“A regulation like DORA or NIS2 now applies to us, and we don’t know where to start.”
Flagship services
Two engagements most companies start with.
Cyber Assurance Assessment
Understand your cyber risk before investing in more technology. A structured maturity and posture assessment, gap analysis ranked by risk, board-level reporting and a prioritised improvement roadmap.
ExploreVirtual CISO (vCISO)
Strategic security leadership without the cost of a full-time CISO. A named senior advisor, provided through a vetted specialist partner, who owns your governance, strategy, risk and board reporting on a retained basis.
ExploreWhat else advisory covers
Named engagements, not open-ended consulting.
Board-level risk assessment
Your risks set out in business terms, with likelihood, impact and the cost to fix, so the board can decide what to fund with its eyes open.
Prioritised remediation roadmap
A sequenced 12 to 24 month plan that tackles the highest risks first and fits the budget and the people you actually have.
Regulatory & certification readiness
Get ready for what clients and regulators now ask for: ISO 27001, SOC 2, DORA and NIS2, plus preparation for the EU AI Act.
Incident readiness review
A straight test of whether you could really respond: a response plan, defined roles and a tabletop exercise with your leadership team.
Cyber security strategy
A security strategy tied to what the business is trying to do, with clear ownership and the measures the board will see each quarter.
Supplier security review
Which suppliers could hurt you most, what you have asked of them and what to tighten in contracts and onboarding.
AI governance has its own home under Compliance: helping you govern your own use of AI and prepare for the EU AI Act.
What you walk away with
Documents you can act on, not a slide deck.
- A posture scorecard against your chosen framework, every gap ranked by risk
- A board-ready risk register your leadership can act on
- A costed, prioritised remediation roadmap you can actually resource
- A straight recommendation on what to keep, what to change and what to drop
- One accountable point of contact at Threat Protect, start to finish
Who does the work
Senior consultants, one point of accountability
Advisory work is delivered by vetted specialist partners, matched to your sector and the frameworks you need. Our partners include firms holding NCSC Assured Cyber Security Consultancy or Cyber Advisor status.
Threat Protect runs the process. We scope the engagement, choose the partner, manage the commercials, check the quality of the output and stay accountable for the result. You have one relationship to manage, however many specialists the work needs.
Which help you need
Consultant, vendor or managed service?
These three are often sold as if they were the same thing. They answer different questions, and most organisations need the first before they can choose the other two well.
| The question it answers | What you get | |
|---|---|---|
| Cyber security consultant | Where are we exposed, and what should we do first? | Independent advice, a risk picture and a plan |
| Technology vendor | How does this product solve a problem? | A tool, and advice about that tool |
| Managed security provider | Who watches our systems day and night? | Ongoing monitoring and response |
Frameworks and regulation
Advice that maps to what you are measured against
Partners work against the framework that matches your situation: ISO 27001, the NIST Cybersecurity Framework, the NCSC Cyber Assessment Framework or the CIS Controls. If a regulation or a customer sets the standard, the work maps to that instead.
If certification is the goal, it is delivered through certified assessment partners. Threat Protect does not issue certificates itself.
Board reporting
Giving the board an answer it can use
The UK government’s 2025/26 Cyber Security Breaches Survey found that 68% of large businesses have a board member responsible for cyber security, against 31% of businesses overall. Boards increasingly ask for an answer, and alert counts do not give them one.
A good consultant reports cyber risk as money, downtime and regulatory exposure, with a trend the board can follow from one quarter to the next.
Choosing well
How to choose a cyber security consultant
Six checks will separate most firms, whoever you end up choosing.
- Independence: are they tied to one vendor, and what would they recommend if it were not on their price list?
- Named people: who will actually do the work, and can you speak to them before you sign?
- Credentials: look for recognised schemes such as NCSC Assured Cyber Security Consultancy and Cyber Advisor, and individual qualifications such as CISSP, CISM or ISO 27001 Lead Auditor.
- Sector experience: have they worked under your regulator and with customers like yours?
- A sample deliverable: ask to see an anonymised report and roadmap, not just a slide about them.
- What happens next: can they help you act on the plan, without obliging you to buy from them?
Cost
What cyber security consultancy costs
Pricing is on application, because scope varies so widely. We scope it on a short call and quote before any work starts, so you know what you are buying.
- The size of the organisation, and the number of sites and business units in scope
- Which framework or regulation the work maps to
- How much evidence and how many interviews are needed
- Whether you need a one-off engagement or ongoing leadership
- How senior or specialised the consultant needs to be
Where it leads
Advisory is the start of the conversation, not the end.
FAQ
Questions buyers actually ask
What does a cyber security consultant do?
A cyber security consultant assesses an organisation’s security risk, explains it in business terms and sets out what to fix first. Typical work includes maturity assessments, risk registers, security strategy, board reporting, regulatory readiness and incident response planning. The output is a decision and a plan, not a tool.What is the difference between cyber security advisory and consulting?
In practice the terms overlap. Advisory usually means ongoing senior guidance, such as a virtual CISO. Consulting usually means a defined piece of work, such as an assessment or a roadmap. Many organisations start with a one-off engagement and move to ongoing advice once the plan is in place.How much does a cyber security consultancy cost?
Threat Protect’s pricing is on application. Cost depends on the size of the organisation, the sites in scope, the framework, the depth of evidence needed and whether the work is one-off or ongoing. We scope it on a short call and quote before any work starts.Who delivers Threat Protect’s advisory work?
Vetted specialist partners deliver the work, matched to your sector and frameworks. They include firms holding NCSC Assured Cyber Security Consultancy or Cyber Advisor status. Threat Protect scopes the engagement, selects and contracts the partner, oversees delivery and remains your single point of accountability.Do we have to buy technology through you afterwards?
No. You own the roadmap and can act on it however you choose. If you want help, we can source what it calls for and run the process, and you decide at each step.Which sectors do you work with?
All sectors. Our focus is on organisations of 250 or more staff, especially regulated sectors where the pressure is highest, such as finance, legal, energy, pharma, healthcare and manufacturing. We also support smaller organisations and schools.
Start with an honest read of where you are.
A 30-minute call with a senior advisor. Bring your situation; leave with at least one useful answer, whether or not we’re a fit.
Book a call Also available in AWS Marketplace