Advisory · Virtual CISO
Virtual CISO (vCISO) services
A CISO on your team, not on your payroll. A named senior advisor, provided through a vetted specialist partner, who owns your security strategy, runs your risk reviews and fronts security to your board, on a retained basis and scaled to what you actually need.

Definition
What is a virtual CISO?
A virtual CISO (vCISO) is an experienced security leader who does the work of a chief information security officer on a part-time, retained basis. They own your security strategy, risk register, policies and board reporting, usually for a set number of days a month. You may also hear it called CISO as a service, or a fractional CISO.
A vCISO leads and decides. They do not replace your IT team or a security operations centre, and accountability for cyber risk stays with your board.
| What it is | Best when | |
|---|---|---|
| Virtual CISO | Retained senior leadership, usually from a specialist firm | You need the leadership, but not five days a week |
| Fractional CISO | Often the same thing: a set share of a CISO’s time | The term is mostly used interchangeably with vCISO |
| Interim CISO | Full-time cover for a fixed period | You are between hires, or running a major programme |
| Full-time CISO | A permanent executive on your payroll | Security is a daily, hands-on leadership job |
When it fits
A vCISO is not a discount CISO.
It is the right shape of leadership for a particular stage. Here is the honest read on when each one makes sense, including when you should just go and hire.
A full-time CISO fits when
- Security is core to your product and a daily, hands-on concern.
- You have a security team that needs a leader in the building every day.
- Regulatory scrutiny demands a single named executive on staff.
- The role is comfortably a full-time job, and then some.
A vCISO fits when
- You typically have 250+ staff, or you are a smaller regulated firm, and security has outgrown a side job.
- You need senior direction and a credible board voice, not another tool.
- You want that leadership now, not after a six to nine month search.
- The work is real, but does not yet justify a full-time hire.
What your vCISO owns
Leadership across the things that move the needle.
Governance & policy
Ownership of your security governance and the policies that sit beneath it.
Strategy & roadmap
A security strategy and forward plan the board can understand and get behind.
Board reporting
Clear reporting that gives your board and clients confidence.
Risk management
A live risk register, kept current, with risks framed in business terms.
Planning & budget
Security planning and budget ownership, so spend follows the real priorities.
Incident readiness
A response plan, clear roles and rehearsals, so leadership knows its part before anything goes wrong.
How it works
What a vCISO does in the first 90 days
Set the direction first, then keep a hand on the tiller. A typical engagement runs like this, adjusted to what you already have in place.
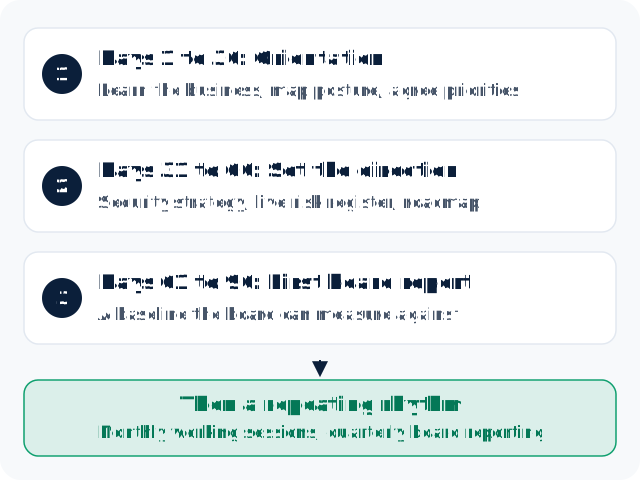
1.Days 1 to 30: orientation
Your vCISO learns the business, maps your current posture and agrees what matters most.
2.Days 31 to 60: set the direction
They set the strategy, stand up or refresh your risk register and agree a roadmap.
3.Days 61 to 90: first board report
The board gets a baseline it can measure against, and a clear view of what is being funded and why.
4.Every month
Working sessions to drive the roadmap, make the calls and keep momentum between board cycles.
5.Every quarter
Board-level reporting, a re-baselined risk picture and the next quarter’s priorities.
Who you work with
Who your vCISO is
Your vCISO is a named senior advisor, provided through a vetted specialist partner and matched to your sector and frameworks. You will know who it is before you commit.
Threat Protect runs the process. We select and contract the advisor, oversee the engagement and stay your single point of accountability. If the fit is wrong, you have one call to make.
Why boards ask for one
What a vCISO gives the board
The UK government’s 2025/26 Cyber Security Breaches Survey found that 68% of large businesses have a board member responsible for cyber security. That person needs someone who can tell them what the risk is, whether it is falling and what the next pound should buy.
A vCISO also fronts the conversations that otherwise land on your IT lead: customer security questionnaires, auditors, insurers and regulators.
Cost
What a virtual CISO costs
Pricing is on application, because the time you need depends on what you are trying to do. These are the things that move it.
- How many days a month you need, and whether that changes after the first 90 days
- Your size, complexity and number of sites
- Your regulatory position, such as FCA oversight, DORA or NIS2
- Whether you are working towards a certification such as ISO 27001
- How much board, customer and auditor contact the role involves
| Full-time CISO | Virtual CISO | |
|---|---|---|
| Pay | Salary, bonus, employer costs and benefits | A retainer, for the time you use |
| Time to start | Often a six to nine month search | Usually much sooner |
| Breadth | One person’s experience | A partner’s wider bench behind them |
| Presence | In the business every day | Set days, plus agreed availability |
Market context
What a full-time CISO costs in the UK
The median advertised salary for a UK CISO was £100,000 in the six months to 6 November 2026, according to ITJobsWatch. That is based on job adverts, so it is a guide only, and senior roles in regulated firms can pay well above it. Bonus, pension, employer’s National Insurance and recruitment fees all come on top.
Choosing well
How to choose a vCISO service
A vCISO will speak for you in front of your board and your customers, so check more than the CV.
- Can you meet the named person, and will the same person stay with you?
- Have they led security in your sector, and under your regulator?
- Are they tied to a vendor, or free to recommend what fits?
- Have they presented to a board? Ask to see an anonymised board report.
- What happens if they are unavailable during an incident?
- Is the scope written down, including how many days and what is out of scope?
Where it leads
Leadership that can call on delivery when you need it.
Because Threat Protect can also source what the strategy calls for, your vCISO’s plan is never just advice left on a shelf. That includes ISO 27001 support when a client or regulator asks for certification.
FAQ
Questions buyers actually ask
What does a virtual CISO do?
A virtual CISO owns an organisation’s security strategy, governance, policies, risk register, budget planning and board reporting on a part-time, retained basis. They also prepare leadership for incidents and front conversations with customers, auditors, insurers and regulators.What is the difference between a vCISO and a fractional CISO?
Very little. Both mean part-time senior security leadership, and most providers use the terms interchangeably, along with CISO as a service. Check the scope rather than the label: how many days, which named person and what they are accountable for.How much does a virtual CISO cost?
Threat Protect’s pricing is on application. Cost depends mainly on the number of days a month, your size and complexity, your regulatory position and whether you are working towards a certification. We scope it on a short call.How many days a month does a vCISO need?
It depends on your size, your regulators and how much is already in place. Many engagements need more time in the first 90 days, while the strategy and risk register are set up, then settle into a lighter monthly rhythm. We agree the time at scoping and review it as things change.Who provides the vCISO?
A named senior advisor, provided through a vetted specialist partner and matched to your sector and frameworks. Threat Protect selects and contracts the advisor, oversees the engagement and remains your single point of accountability.Does a vCISO take on legal accountability for our security?
No. Accountability for cyber risk stays with your board and any regulated senior managers. A vCISO gives them the advice, plan and reporting they need to carry that responsibility, and helps them show how it is being met.Does a vCISO respond to incidents?
A vCISO leads the decisions and the communication with your board, but hands-on forensic work sits with an incident response specialist. Part of the role is making sure that specialist is lined up before you need them, and that leadership has rehearsed.When should we hire a full-time CISO instead?
When security is a daily, hands-on leadership job: a security team that needs a leader every day, security at the core of your product, or a regulator that expects a named executive on staff. Many organisations use a vCISO first, and the vCISO can help write the job description when the time comes.
Strategic security leadership, on tap.
Tell us where security sits in your company today. We’ll show you what a vCISO engagement would look like.
Book a call Also available in AWS Marketplace