Your Security Buyer
Your Security Buyer: independent security sourcing
Make us your first call, not the vendor’s. Buying security usually means fielding pushy vendors, sitting through demos and somehow judging it all yourself. We take that off your desk. Brief us once on the objective or the risk, and we do the legwork.

Definition
What is independent security sourcing?
Independent security sourcing means someone who is not tied to one vendor finds, compares and negotiates your security services for you. You describe the objective or the risk. They work out what would solve it, go to market and bring back a like-for-like comparison, so you can decide without sitting through every sales process.
Threat Protect does this as your security buyer. We are vendor-agnostic, so we can recommend from across the market, and we stay your single point of accountability after the contract is signed.
How it works
Tell us the goal. We take it from there.
- 01Tell us the goalBring us an objective you need to land with the board, or a risk you need to mitigate. No spec, no shortlist and no vendor names required.
- 02We adviseYou get experienced, independent advice on what actually solves it, before anyone talks product. Often that means less than you were about to buy.
- 03We source & negotiateWe go to market, shortlist the best-fit services and handle every vendor conversation and negotiation for you, at preferential partner rates.
- 04We present the optionsYou get a clear, like-for-like comparison and a straight recommendation. You decide. We handle the contracts and the onboarding.
What we source
Services and subscriptions.
Almost everything we source is a service or a subscription: chosen, negotiated and set up, with specialists running the tools and Threat Protect running the process. From a single point solution to a full programme.
Managed security & SOC
Round-the-clock detection and response from a specialist provider, with us running the process.
Continuous compliance
Subscription GRC platforms and certified assessment that keep you audit-ready.
Email & collaboration security
Cover where most attacks still begin: phishing, impersonation, spoofing.
Endpoint & device protection
Laptops, servers and mobile, protected by a service we select and oversee.
Identity & access
MFA, conditional access and identity hygiene to shut down account takeover.
Awareness training
Programmes that turn your people into a control, not the weak link.
Cyber insurance
Cover introduced through a regulated broker, plus help with the controls insurers now expect.
Advisory & vCISO
Senior security leadership on tap, through vetted partners, scoped to what you actually need.
Vendors we source from
We hold partner agreements across the market. That is how we secure preferential rates and stay free to recommend what genuinely fits, rather than what we’re tied to. A sample of who we work with:
All 33 of our services can be bought through your AWS account, on the AWS bill you already pay.
Browse the services


Don’t get caught in the sales trap
Going direct, versus going through us.
Going direct
Through Threat Protect
Choosing well
How to choose a cyber security vendor
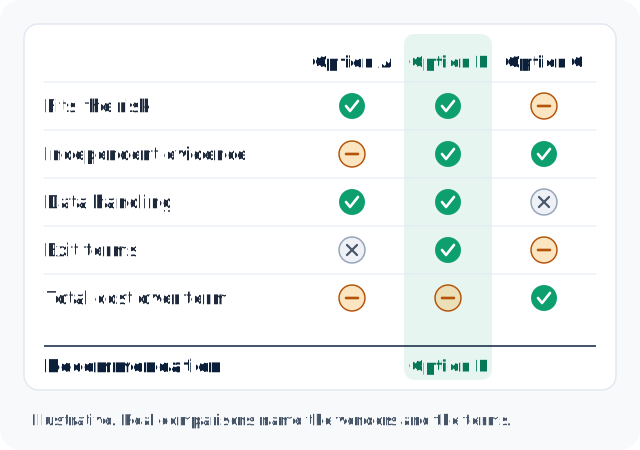
Start with the risk, not the product list. Whether you buy through us or on your own, these are the checks that separate the options, and the ones we put in front of you.
1.Does it fit the risk?
Write down the risk or the objective first. If a vendor cannot show how it closes that specific gap, the feature list does not matter.
2.What is the independent evidence?
Look for third-party testing, named references in your sector and certifications that cover the service you are buying, not just the company.
3.Where does your data go?
Ask where data is held and processed, who can reach it, and which sub-processors are involved. Your own auditors and customers may ask the same.
4.How hard is it to leave?
Check the notice period, the renewal terms, what happens to your data and how long a move would take.
5.What is the total cost over the term?
Compare the whole term, including onboarding, the people needed to run it, overlap with tools you already own and any uplift at renewal.
An honest answer
When going direct makes sense
You do not always need a buyer. Going direct can be the right call in some situations, and we will tell you if yours is one of them.
- You know exactly what you want, and you have the time to run the process
- You have a security-literate procurement team that negotiates this category regularly
- You already hold an enterprise agreement that makes the product hard to beat
Beyond the first purchase
Renewals and tool consolidation
Security stacks tend to grow one urgent purchase at a time. The result is overlapping tools, features nobody has switched on and renewals that arrive with little warning.
We can review what you already hold, show where tools overlap, and take renewals to market with enough notice to make a difference. Sometimes the best recommendation is to keep what you have and use more of it.
Where it leads
Buying is one part of the relationship.
FAQ
Questions buyers actually ask
What does an outsourced security buyer do?
An outsourced security buyer takes your objective or risk, advises on what would solve it, goes to market, handles the vendor conversations and negotiation, and presents a like-for-like comparison with a recommendation. You make the decision.Is it cheaper to buy through Threat Protect than to go direct?
Often, yes. We buy at preferential partner rates, and you see the options like for like. It is not guaranteed for every product, and if you already hold a strong agreement with a vendor, we will say so.Do we have to replace our existing vendors?
No. Many engagements start with one specific need or an upcoming renewal. If what you have is doing the job, the recommendation may be to keep it.Can we say no to your recommendation?
Yes. You get the options and the reasoning, and you decide. You are not obliged to buy anything as a result of asking us to look.What can you source?
Mostly services and subscriptions: managed security and SOC, continuous compliance platforms, email, endpoint and identity security, awareness training and advisory. Cyber insurance is introduced through a regulated broker.Who is accountable once the service is live?
Threat Protect stays your single point of accountability. Specialist vendors and partners deliver the services, and we run the process around them, from onboarding through to reviews and renewal.
One call. We source the rest.
Tell us the objective or the risk you’re trying to close out. We’ll come back with experienced advice and the best-fit options, negotiated for you.
Book a call Also available in AWS Marketplace