Trust, but verify
Penetration testing services
Independent penetration testing across your infrastructure, web applications, cloud and Microsoft 365, delivered through CREST accredited partners. Not a compliance tick-box: proof that the controls you have paid for actually hold, with every fix retested and the proof kept up between tests.

Definition
What is penetration testing?
A penetration test is an authorised, simulated attack on your systems by a qualified tester. It finds the weaknesses a real attacker could exploit, and proves what they would lead to.
It is not a vulnerability scan. A scan lists what might be wrong. A penetration test establishes what is actually exploitable, chains those weaknesses together the way an attacker would, and shows you the business consequence at the end of the chain.
The output is evidence: what was found, how it was proven, what it would mean for your organisation, and what to fix first.
| What it does | How often | |
|---|---|---|
| Vulnerability scan | Automated. Lists possible weaknesses, with no proof that they can be exploited | Weekly or monthly |
| Vulnerability assessment | A scan plus expert validation and prioritisation, still without exploitation | Monthly or quarterly |
| Penetration test | Human-led. Proves what is exploitable and what it leads to | Annually, and after major change |
| Continuous validation | Automated and safe. Repeats the proof between tests as your environment changes | Monthly, or on change |
Related
Infrastructure
Infrastructure penetration testing
Your networks, servers, firewalls and the remote access everyone forgot about, tested from the outside and from the inside. This is where most organisations should start, and where most real attacks begin.
External penetration testing
Your internet-facing estate, probed the way an attacker finds it: exposed services, unpatched edge devices, the VPN appliance and the forgotten subdomain. Edge devices and VPN appliances are now a common route into UK organisations, so they get particular attention.
Internal penetration testing
The question that matters more. Once someone is inside, through a phish, a stolen credential or a contractor’s laptop, how far can they get? This is where Active Directory weaknesses, flat networks and over-privileged accounts turn a small incident into a large one.
Wireless penetration testing
Your wireless networks, guest segregation and the assumption that your corporate Wi-Fi cannot be reached from the car park.
Applications
Web application, API and mobile penetration testing
Applications tested properly, which means logged in. Most application testing stops at the login page, and almost all of the interesting risk is on the other side of it.
Web application and API penetration testing
Web application penetration testing looks for broken access control, one user reaching another user’s records, business logic that can be walked around and authentication that can be bypassed. It is tested against the OWASP Top 10 and well beyond it.
The APIs behind the application are tested too, including REST, GraphQL and SOAP endpoints, because that is usually where the real attack surface lives.
Mobile application penetration testing
iOS and Android applications, the data they store on the device, and the APIs they talk to.
Source code review
A specialist review of the code itself. It finds the flaws that are hard to see from the outside: insecure handling of input, secrets left in code, weak cryptography and logic errors. Useful before a major release, and alongside an application test rather than instead of one.
Cloud and identity
Cloud, identity and Microsoft 365 testing
Identity is where most attacks turn from an incident into a breach. A stolen credential is not the end of an attack, it is the middle of one. It is the point where someone stops being outside your business and becomes a user inside it, with whatever that user can reach.
Cloud penetration testing
Misconfiguration and over-permissioned access across AWS, Microsoft Azure and Google Cloud: identity paths, storage exposure and privilege escalation between accounts. The most common modern weakness, and the one a traditional network test is least likely to catch.
Identity and Active Directory testing
Weak, reused and already-breached credentials, Active Directory misconfiguration, privilege escalation paths, and what a working set of credentials reaches across your estate. Much of this involves no software vulnerability at all, which is why a scanner rarely finds it.
Microsoft 365 security reviews
A focused review of your tenant: identity, conditional access, legacy authentication, sharing settings, privileged roles and the configuration attackers exploit most often.
Hardware and IoT penetration testing
Connected devices and the firmware, interfaces and configuration behind them, probed for the weaknesses attackers physically exploit.
Your AI
AI and LLM application testing
Have you built or deployed AI features, such as a customer chatbot, an internal copilot or an assistant connected to your documents? Then they are part of your attack surface, and need testing like any other application.
Testing covers prompt injection, leakage of data the model can see, unsafe handling of what the model returns, and AI features given more permissions than they need. The OWASP Top 10 for LLM Applications is the baseline. The findings feed straight into how you govern AI across the organisation.
Related
People and objectives
Red teaming and social engineering
Some questions are about people and response rather than systems. These engagements answer them.
Social engineering and phishing assessments
Phishing, phone-based pretexting and other approaches that test how your people respond, and more importantly what a working set of stolen credentials would actually reach.
Red teaming
A goal-driven exercise that tests whether your detection and response would catch a determined attacker pursuing a specific objective. It is not a bigger penetration test. If your tests keep returning the same findings, fixing them comes first.
Threat-led penetration testing
Intelligence-led testing modelled on real threat actors, as required of certain financial entities under DORA, and run under frameworks such as CBEST and TIBER-EU.
The chain
Your web application is a front door, not a destination.
Almost nobody attacks an application for its own sake. They attack it because of what it is connected to. The shape of a real incident is dull rather than dramatic.
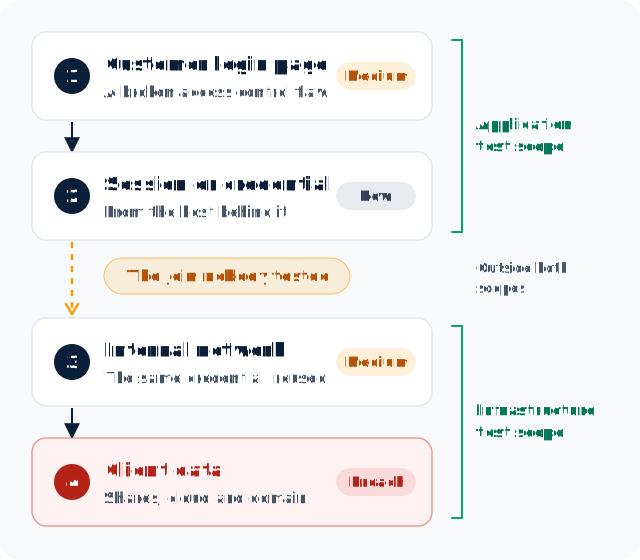
Why testing in silos misses it
Not one of those steps is a zero-day. Each one, on its own, would be rated low or medium and sit near the bottom of a remediation list. Together they are the whole breach.
Buy an application test and you learn about the application. Buy an infrastructure test and you learn about the infrastructure. Neither tells you that step two connects to step three, because that join sits outside both scopes. Nothing in the reports was wrong. The gap was between them.
What gets tested instead
Application, infrastructure, cloud and identity scoped as one connected estate, so the question is not “is this application secure” but “what can someone reach from here, and does it matter”.
The finding that changes a board’s mind is never a CVE number. It is a diagram showing the route from a public login page to the thing that would stop the business.
CREST
CREST accredited testing, and what the badge covers
Our penetration testing is delivered through CREST accredited partners, and several hold further specialist accreditations for work that calls for them. It is worth being precise about what CREST means, because the badge is widely asked for and less widely understood.
Organisations and testers, not software
CREST accredits organisations and certifies individual testers. An accredited company has been externally assessed on its methodology, data handling, personnel vetting and reporting, and is reassessed to keep it. Certified testers have passed CREST’s examinations, which at the senior levels are practical and hands-on.
CREST does not accredit software on its own. Some automated testing platforms are sold as part of an accredited provider’s service, where the provider’s testers review and validate what the platform finds before the report is issued. The accreditation then covers that service and the people behind it, not the tool. If you are quoted CREST for an automated test, ask whether a qualified tester reviews the findings, how long that takes, and which accreditation covers the service.
What accreditation gives you
An externally assessed provider, examined testers, a recognised methodology, and a signed report that auditors, insurers and enterprise procurement teams accept without argument.
What it does not give you
Any coverage between tests, and any confirmation that the findings were ever closed. That second point is the one most organisations discover too late.
Point in time
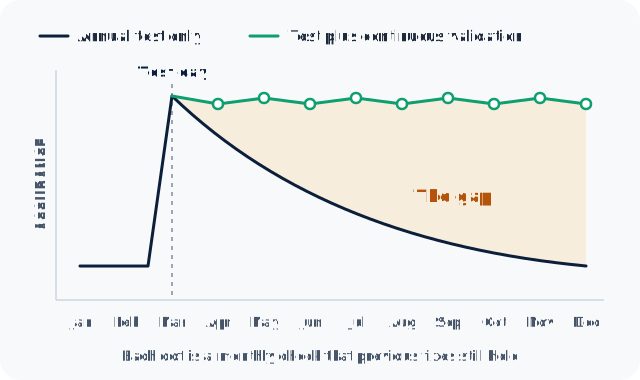
A test proves what was true on the day it ran.
A penetration test is a photograph: a good one, taken by a professional, of the things that mattered on the days they looked. Then the year happens. You patch some things and miss others. A supplier gets integrated. A firewall rule gets widened for a weekend and never narrowed. Your developers ship a dozen releases. A new vulnerability is disclosed in something you run.
None of that is negligence. It is what running an organisation looks like. But it means the report describes an estate that no longer exists, and the gap widens every week.
1.How many of the findings are actually closed?
Most organisations have a remediation spreadsheet, a set of assurances, and no independent verification.
2.Who confirmed they were closed?
Retests are usually chargeable and often skipped, so the test was paid for and whether its findings were fixed was never checked. That is not a criticism of the tester: verification sat outside the engagement. It is simply a gap, and it is the one we close.
3.What has changed since?
If you release monthly, a report from March describes software you no longer run.
Between tests
Tested by people. Proven all year.
The answer is not to replace penetration testing with automation. Anyone selling you that is overstating what automation does. The answer is to stop spending expensive human days on work automation now does well, and spend them on work only a person can do.
Continuous validation runs on an automated testing platform that we select and oversee for you, safely and in production, between your accredited tests. Route discovery, injection classes, credential auditing, known vulnerability exploitation and external sweeps run on a regular cadence. The accredited test then narrows and deepens. Your tester spends the days on access design, multi-step business logic and the workflows that would hurt your business. They do not spend them re-mapping what the platform already found.
- New and changed systems appearing on your estate
- Whether previous findings are still closed
- Exposure to newly disclosed vulnerabilities, tested rather than assumed
- Credential and Active Directory weaknesses as accounts change
- Whether your endpoint protection blocks what it claims to
| Continuous validation | Penetration testing | |
|---|---|---|
| Runs | Monthly, or on change | Annually, or as compliance requires |
| Best at | Breadth, repetition and verification | Depth, creativity and judgement |
| Finds | Known weaknesses, attack paths, drift and new exposure | Business logic flaws, chained reasoning and the unexpected |
| Proves | That fixes landed and stayed landed | That a skilled person could not get through |
| Gives you | A current picture and a trend line | A signed report for auditors and insurers |
| Delivered by | An automated platform we select and oversee | CREST accredited testers |
Process
How a penetration test runs
1.Scope
A short conversation about what you run, what would hurt most if it stopped, and what you are being asked to prove. We will tell you if a smaller scope would answer the question just as well.
2.Authorise
Written rules of engagement, signed by someone with authority over every system in scope. Testing without that authorisation can be an offence under the Computer Misuse Act 1990, so this is not paperwork for its own sake.
3.Reconnaissance and mapping
What is actually there, which is rarely what the asset register says.
4.Exploitation
Proving what can be reached and what it leads to, within agreed limits and without taking anything down.
5.Report and debrief
Findings with evidence, ranked by business impact, with a walkthrough for the people who have to fix them.
6.Retest and verify
Confirmation that what you fixed is actually fixed, with a date against it. Many providers stop at the report. This is the step that matters to your auditor.
The report
What you receive from a penetration test
- An executive summary a non-technical board member can read in one page and act on
- Findings ranked by business impact, not raw severity score, because a medium that reaches client data matters more than a high that reaches nothing
- Evidence for every finding: the route, the proof and the screenshot, so nobody argues about whether it is real
- A prioritised remediation plan, ordered to break the most attack paths first
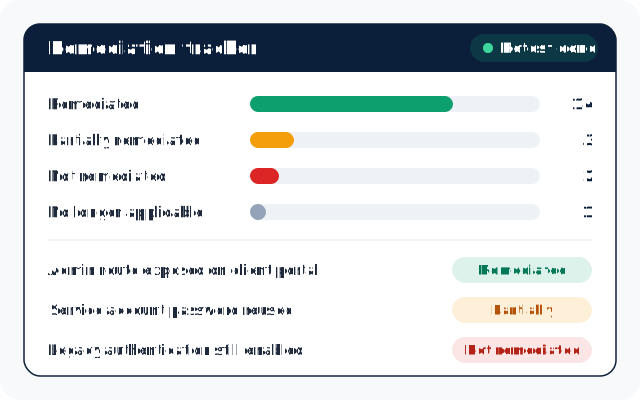
- A retest and a verification record, so you can show an auditor what was closed and when
- A debrief with the people who have to do the work
| Status | Meaning |
|---|---|
| Remediated | Confirmed fixed on retest |
| Partially remediated | Risk reduced, but residual risk remains |
| Not remediated | Still present or still exploitable |
| No longer applicable | The affected system or configuration is gone |
Compliance
When a framework, insurer or client requires a test
Most penetration tests are bought because a third party asked for one. Knowing exactly what they asked for usually saves money.
ISO 27001
ISO 27001 does not name penetration testing, but it expects you to manage technical vulnerabilities (Annex A 8.8) and test security in development (8.29). A test is the most common evidence, and the auditor is at least as interested in whether the findings were closed.
SOC 2
A SOC 2 Type 2 report covers a period of time, so evidence that controls held across the period carries more weight than a single snapshot taken at the start of it.
PCI DSS
PCI DSS v4.0.1 requires internal and external penetration testing, segmentation testing and, under requirement 11.4.4, that exploitable vulnerabilities are corrected and testing repeated to verify the corrections.
DORA
DORA requires in-scope financial entities to test their ICT regularly, and the most significant, as designated by their regulator, to run threat-led penetration testing at least every three years. The same expectations are pushed onto suppliers, including UK firms serving EU clients.
Cyber Essentials and Cyber Essentials Plus
Neither requires a penetration test. Cyber Essentials Plus includes a technical audit with vulnerability scanning, which is narrower. What both require is that the five controls hold, and testing is a reasonable way to know they do.
UK GDPR
Article 32 expects a process for regularly testing, assessing and evaluating the effectiveness of your security measures. “Regularly” is doing a lot of work in that sentence.
Cyber insurance
Renewals increasingly ask whether you test and how often. Answer accurately. A test scoped to your external estate should not be described to an underwriter as a general one. A misrepresentation can be revisited at exactly the moment you need to claim.
Client due diligence
Supplier questionnaires and client security reviews are, in practice, the most common driver of all.
Terms explained
Security testing terms, decoded
This market generates acronyms faster than it generates clarity. If you have been handed one by an analyst, a vendor or your board, here is what each means and where it sits relative to a penetration test.
Penetration testing as a service (PTaaS)
Penetration testing bought on subscription and delivered through a platform, rather than as a one-off project with a PDF at the end. The testing is still human. What changes is the commercial model and how you receive findings: a portal, live status, and usually retesting included.
Continuous penetration testing
PTaaS with a regular cadence rather than one annual engagement, usually automated testing throughout the year with human testing at intervals.
Automated or autonomous penetration testing
Software that executes real attack techniques without a person driving each step. Useful for breadth, repetition and verification. It does not replace a human tester, and the software itself is not CREST accredited.
Breach and attack simulation (BAS)
Software that runs simulated attack behaviour to check whether your detection and response tooling notices. It validates your defences rather than proving your exposure, so it is often bought alongside a test rather than instead of one.
Adversarial exposure validation (AEV)
A category Gartner introduced in 2025 for technologies that give continuous, automated evidence that an attack is feasible. It brings together tools previously sold as breach and attack simulation and automated penetration testing.
Continuous threat exposure management (CTEM)
Gartner’s five-stage operating model: scope, discover, prioritise, validate and mobilise. It is not a product. Most organisations have tooling for discover and prioritise and nothing for validate, which is the stage that tells you whether any of it matters.
Attack surface management (ASM)
Continuous discovery of what you expose to the internet, including the things nobody told you about. It tells you what exists, not what is exploitable.
Where Threat Protect sits
CREST accredited penetration testing through accredited partners, plus continuous validation between tests across infrastructure, web applications, cloud and identity. In analyst terms, that is the validate stage of a CTEM programme. Put simply: people prove depth once, automation proves the rest holds all year, and every fix is verified. Red teaming and threat-led testing are arranged when the requirement calls for them, which is less often than they are proposed.
Cost
How much does penetration testing cost in the UK?
Penetration testing is priced on application: we scope first, then quote. The quote comes down to the number of testing days, and the testing days come from the scope. A focused external test is a small engagement; a full internal, application and cloud assessment is a much larger one.
Accredited day rates vary across the market. Treat a quote far below the going rate with caution: it is often an automated scan with a report template on top.
- The number of live hosts and external IP addresses
- The number of applications, and whether they are tested logged in
- How many user roles need testing separately
- Whether cloud, identity and Microsoft 365 are in scope
- Whether a retest is included, and it should be
How to spend less without getting less
Scope to the question you are actually being asked. If an insurer wants to know your external estate is tested, that is a different and much smaller engagement than a full assessment. Start there and widen where the risk is, rather than buying the largest scope on offer.
And if the same findings reappear year after year, the answer is not a bigger test. It is verification between tests.
Who delivers it
Independent testing, joined up with remediation
Our penetration testing services are delivered by CREST accredited partners that we select, brief and oversee. They are independent of the people who build and run your defences, so the validation is impartial. Between them they cover the full range of offensive security, from a focused external test to red teaming.
We scope the work, sit with the findings and turn every result into action: feeding it into your roadmap and, where you want it, managed security. We are vendor-agnostic by design, so we have no product to defend when a finding points at something you already bought. One relationship, with testing, remediation and the evidence to prove both. We provide penetration testing across the UK, with on-site meetings in London and the South East where they help.
FAQ
Questions buyers actually ask
What is the difference between a penetration test and a vulnerability scan?
A scan is automated and lists weaknesses that might exist. A penetration test is human-led and proves which weaknesses are actually exploitable and what they lead to. A scan might return thousands of findings; a test returns the handful that matter, with evidence.How often should we have a penetration test?
Most organisations test annually, and most compliance frameworks assume that. The right frequency depends on how often your environment changes. If you ship software monthly or your estate is growing, an annual test leaves a long gap, which is why continuous validation between tests is worth considering.How much does penetration testing cost in the UK?
It is priced on application, because scope drives the price more than anything else. The cost comes down to testing days, which depend on the number of hosts and applications, how many user roles are tested and whether cloud and identity are in scope. A focused external test is a small engagement; a full assessment is a larger one. We scope first and quote once the scope is agreed.Is CREST accreditation required?
Not legally, but many insurers, enterprise procurement teams and public sector buyers ask for it, and it is a reasonable proxy for quality. CREST accredits organisations and certifies individual testers. It does not accredit software on its own: where an automated platform is sold under CREST, the accreditation covers the provider’s service and the testers who review the results.Will testing take our systems down?
It should not, and limits are agreed with you beforehand. Destructive techniques such as denial of service are excluded unless you specifically ask for them, and rules of engagement are agreed in writing before anything starts.Do we need a penetration test for Cyber Essentials?
No. Cyber Essentials and Cyber Essentials Plus do not require one. Cyber Essentials Plus includes a technical audit with vulnerability scanning, which is a different and narrower thing, so a penetration test is not mandatory for certification.What is PTaaS, and is it different from a penetration test?
PTaaS, or penetration testing as a service, is penetration testing bought on subscription and delivered through a platform rather than as a one-off project. The testing itself is still human-led. What changes is the commercial model, the cadence and how you receive findings: usually a portal with live status rather than a PDF at the end, with retesting included.Do we need CTEM, or is a penetration test enough?
Continuous threat exposure management (CTEM) is an operating model rather than a product, with five stages: scope, discover, prioritise, validate and mobilise. Most organisations already have tooling for discover and prioritise, and nothing for validate. A penetration test is one form of validation, done once a year. Whether you need the full model depends on how fast your environment changes.Does ISO 27001 require penetration testing?
Not explicitly. ISO 27001 requires you to manage technical vulnerabilities and evaluate the effectiveness of your controls. A penetration test is the most common way organisations evidence that, and auditors generally expect to see either testing or a defensible reason why not.How long does a penetration test take?
Most engagements run three to ten days of testing, plus reporting. A focused external test can take two to three days. From scoping to delivery is typically two to four weeks, depending on availability.What do we need to provide?
Written authorisation from someone with authority over the systems in scope, an agreed scope, and technical contacts. Authenticated testing also needs test accounts for each user role. You receive a prerequisites list at scoping.Can you test our production environment safely?
Yes, and in most cases production is where testing is most useful, because staging rarely matches it. Testing is bounded by agreed rules of engagement, exclusions and testing windows.What happens after the test?
You get a report, a debrief and a prioritised fix list. A retest then confirms the fixes landed. Verification is the part most often skipped, and the part auditors most want to see.Should web applications and infrastructure be tested separately?
They can be scoped separately, but they should be understood together. Attackers rarely stop at the application: a flaw in a web app typically yields a credential or a foothold, which is then used against the infrastructure, cloud or identity behind it. Testing each in isolation means nobody checks the join, which is where many real breaches happen.Is a penetration test the same as a red team exercise?
No. A penetration test finds and proves as many weaknesses as possible in a defined scope. A red team exercise tests whether your detection and response would catch a determined attacker pursuing a specific objective. If your tests keep returning the same findings, a red team is usually the wrong next step; fixing the findings is.What else can you test?
The full range of offensive security, through specialist partners: external, internal and wireless infrastructure, web applications and APIs, mobile apps, source code review, cloud, Active Directory and Microsoft 365, hardware and IoT, AI and LLM applications, social engineering, red teaming and threat-led testing.
Find out whether your defences really hold.
Tell us what you want validated and why. We will scope the right test, at the right size, and make sure the findings get fixed rather than filed.
Book a call Also available in AWS Marketplace